
When more code or data is entered into a system buffer than the system was designed to handle, a program security vulnerability known as a Buffer Overflow comes up, by which the excess data overwrites the adjacent memory section of the system; therefore, in such a system, this occurrence creates an influence. Additionally, this concept is both straightforward and highly complex. But let us start with the more specific element, the buffer. Computers use buffers to store data and support your actions when running a program or performing other tasks. When streaming on apps like Spotify, you may be curious as to why your music continues playing for a short period after your network has been disconnected or your connection drops. This is because code was written along with the software to save a portion of data (the music you are playing) in a memory area of your computer called a buffer.
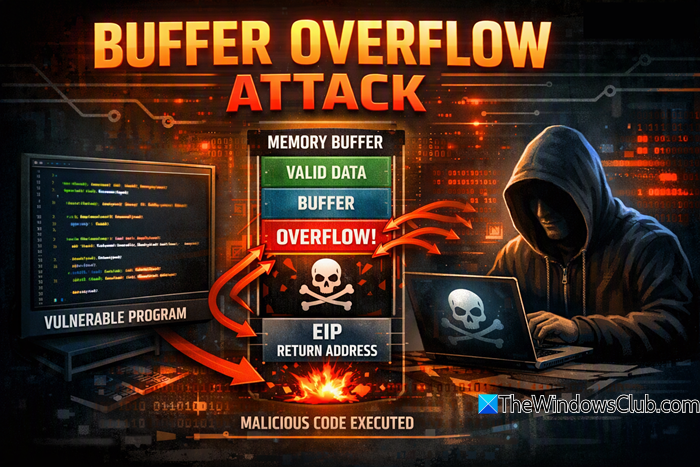
What is Buffer Overflow Attack in cyber security
Buffer Overflow Attacks occur as a result of excess data being input into a system memory buffer. Moreover, when the memory buffer’s capacity has been reached, the music will stop playing. To avoid overwriting other data in your computer’s memory, some programs simply set a limit on how much should be stored in the buffer. However, if you enter more data than the buffer can handle, it may result in various problems on the device running the program or, more likely, a crash. Furthermore, this extra input has the potential to set off a lot of other processes in the system, which could either be based on the desire of the initiator, and this is what Buffer Overflow attack is. This is what Buffer overflows, and buffer overflow attacks are, and there are a variety of causes for them, all of which will be covered in this article.
How do attackers make use of Buffer Overflow vulnerability?
As mentioned, buffer overflow vulnerabilities enable buffer overflow attacks. Depending on the circumstances surrounding the flaw, attackers can exploit a system’s buffer overflow vulnerability in several ways. To put it another way, an attacker will generally add more data to a system in order to overwrite existing data in the system memory or at a returning address.
As a result, the input causes the intended command to execute, which the attacker can use to their advantage or to make your system unstable. The attacker’s primary goal is typically to hijack a program or make it malfunction.
Read: How to report Bug, Issue, or Vulnerability to Microsoft
What causes Buffer Overflow attack?
When faced with a buffer overflow attack, it is essential to know what may be causing the problem. The attack can either be due to a loophole from the programmer’s end or a hacker using the fact that there aren’t limiting parameters to control what could be input into a particular system.
In general, leaving these vulnerabilities and not fixing them up is the basic factor that causes buffer overflow attacks. Besides, if your system doesn’t have a programmed limit of what it should take, you’ll definitely be facing a buffer overflow attack.
Read: What is Replay Attack and how do you prevent it?
Types of Buffer Overflow attack
Buffer overflow attacks can be categorized by where the attacker’s input targets or affects the buffer. Generally, we’ve categorized buffer overflow attacks into:
1] Stack-based buffer overflow attack
A stack-based buffer overflow occurs when an attacker explicitly targets the stack section of memory with their input. This is the most common type of buffer overflow attack and the easier one. Excess input overruns stack memory and hands control of the program to the attacker.
2] Heap-based buffer overflow attack
This type of buffer overflow attack is aimed at another part of a system memory called Heap. This means an attack overwrites data at the heap side of the buffer. Heap-based buffer overflow attack is more brutal compared to the former.
How to prevent Buffer Overflow Attack
Using a programming language resistant to the attack is the most effective way to prevent buffer overflow. C and C++ are highly susceptible to this attack as they don’t have built-in runtime-bound checking features like programming languages such as Python, C#, and Java. Additionally, although buffer overflow faults can be hard to find, you should still review your application and hunt for vulnerabilities carefully.
The following are some methods to stop buffer overflow attacks:
- Keep devices patched
- OS runtime protection
- Use safe programming languages like Java, Python, and C#
- Address space randomization
- Manually testing for buffer overflow
Developers should understand buffer overflow attacks because it helps them identify key concerns when developing a system. It can also help protect you from hacker attacks. This post provides the most thorough discussion of buffer overflow attacks, so please read the entire piece carefully.
Is Buffer Overflow a DoS attack?
Buffer overflow is the most common DoS attack that occurs. The attack happens when more data is input into a system’s memory buffer and, as a result, overwriting data in the nearby memory region.
